

SecInf (Security Infusion)
Cybersecurity teams, security operations analysts and investigators protecting infrastructure and reviewing cyber incidents
Category
Cybersecurity & threat detection
Owner partner
ITML
Related use cases
UC1.4.X
Tool summary
SecInf brings monitoring, threat alerts and historical logs into one view, helping cybersecurity teams spot suspicious activity, examine vulnerabilities and investigate how incidents unfolded.
The challenge
Cybersecurity teams need to understand what is happening across servers, networks and services. Logs and alerts can be scattered across separate systems, making suspicious activity difficult to spot and investigate. Without a shared view of current conditions and past events, teams may struggle to identify threats and reconstruct incidents.
What it does
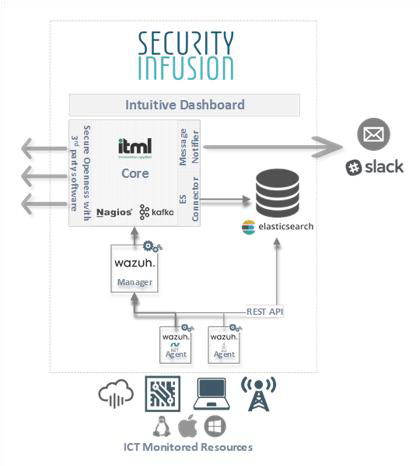
Security Infusion collects security logs, network information and system activity from monitored infrastructure. It brings resource health, threat alerts and vulnerability information into one dashboard, helping teams examine suspicious activity and identify exposed services. Users receive alerts and reports, and can search historical logs to review how an incident unfolded. Within GANNDALF, SecInf provides the monitoring foundation for the wider security investigation workflow, with anomaly detection used to highlight unusual behaviour for analyst review.
Key features
- Continuous infrastructure and service monitoring
- Threat and vulnerability alerts with context
- Unified dashboard for security and resource health
- Searchable historical logs for incident investigation
- Anomaly detection to highlight unusual activity